| TL;DR |
|
A single breach can cost a one-person firm its clients, its reputation, and its standing with the bar. That risk feels enormous, yet almost all of it sits within your control. According to the 2023 ABA Cybersecurity TechReport, 29% of responding firms reported experiencing a security breach, and solo and small firms sit squarely in the crosshairs.
Here is the reassuring part: strong law firm data security is not an enterprise project. It is a set of habits, tools, and choices that fit a solo budget. Let’s walk you through each one, in the order that matters most.
Why Data Security Is a Confidentiality Obligation, Not Just an IT Task
Law firm data security is the set of practices a firm uses to protect confidential client information from unauthorized access, loss, or disclosure. For an attorney, that protection is not a nice-to-have. It is a direct extension of the duty you already owe every client.
Your obligation starts with confidentiality. ABA Model Rule 1.6 requires you to make reasonable efforts to prevent the unauthorized disclosure of, or unauthorized access to, information relating to a client. Storing that information on a laptop or in the cloud does not lower the bar. It raises the stakes.
Competence carries the same weight. Comment 8 to Model Rule 1.1 tells you to keep abreast of the benefits and risks associated with relevant technology. In plain terms, you do not have to become an engineer. You do have to understand the tools you use well enough to protect the clients who trust you with their secrets.
The Real Risks Solo Attorneys Face
Small firms are not too small to target. They are the target. The Verizon 2025 Data Breach Investigations Report found that ransomware was present in 88% of breaches at small businesses, which shoulder that burden far more than large organizations, with a median ransom payment of USD 115,000.
That is a sum most solo practices could never absorb. And it sits well below the ceiling. The IBM 2025 Cost of a Data Breach Report put the global average breach at USD 4.44 million and a record United States average of USD 10.22 million. You will never face the full enterprise figure, but even a fraction of it can end a practice.
Here is where the danger tends to come from:
- AI-assisted phishing, an increasingly common way small firms get breached
- Ransomware that locks up your active case files
- Unsecured public Wi-Fi at courthouses, cafes, and airports
- Cloud misconfiguration that leaves client documents exposed
- AI tools that quietly transmit your input to third-party servers
Basic antivirus no longer covers you. Modern threats call for endpoint detection and response, which watches for suspicious behavior rather than only known viruses. The fallout when defenses fail goes well beyond money: malpractice claims, bar complaints, mandatory client notifications, and reputational damage that follows a solo name for years.
Eight Practical Steps to Secure Client Data on Any Budget
Each step below maps directly to the reasonable efforts standard your bar expects. Start with step one and build from there. You do not need to finish everything this week, only to keep moving.
1. Create a written data security policy
This one is free, and it is where reasonable efforts become visible. A written policy documents what data you collect, where you store it, who can access it, and what happens if something goes wrong. Even a single page counts.
Cover the essentials: device use, passwords, data retention and disposal, remote work, and the security you require from vendors. For a starting framework, lean on the ABA Cybersecurity Legal Task Force resources.
2. Turn on strong passwords and two-factor authentication
Use a password manager such as 1Password, Bitwarden, or Dashlane, most of which run under USD 5 per month. Then enable two-factor authentication on your email, cloud storage, and practice management software. These two habits stop most account takeovers.
The gap here is real. The 2024 ABA Solo and Small Firm TechReport found only about 55% of solos use two-factor authentication and about 52% use file encryption. Closing that gap moves you ahead of nearly half your peers.
3. Encrypt everything, at rest and in transit
Turn on full-disk encryption, which is built in and free: FileVault on Mac, BitLocker on Windows. That protects a lost or stolen laptop instantly. Use email that supports TLS for messages in transit, and share sensitive files through AES-256 encrypted tools instead of plain email attachments.
4. Vet your legal tech vendors
Before you trust a tool with client data, ask hard questions. Does it hold SOC 2 Type II certification? Is data encrypted at rest and in transit? Where are the servers located? What is the breach notification policy, and can you export and delete your data when you leave?
Apply the principle of least privilege: give each tool only the access it needs, nothing more. And remember, you cannot outsource your confidentiality obligation to a vendor. The duty stays with you, as the ABA ethics opinions make clear.
5. Secure your remote work setup
On public Wi-Fi, always use a VPN such as NordVPN or ExpressVPN, both under USD 10 per month. At home, change your router’s default password, enable WPA3 encryption, and set up a separate network for work devices. These small changes close doors that attackers count on being left open.
6. Train yourself and anyone who touches client files
Social engineering, mostly phishing, is one of the top breach patterns for small businesses, and the 2025 Verizon DBIR notes that AI-generated text in malicious emails has doubled in two years. So treat awareness as a security control. Verify any unexpected request involving wire transfers, credentials, or urgent document reviews before you act. Free training from the FTC and KnowBe4 makes this simple.
The same standard applies to anyone who supports you, including a vetted Virtual Legal Assistant. Train them on your policy, and give each person only the access their role requires. The people who touch your files are part of your security posture, not separate from it.
7. Back up your data and test the backups
Set up automated, encrypted backups, and keep at least one copy offline or immutable so ransomware cannot reach it. Then test your restores on a schedule. A backup you have never tested is a guess, and the difference between recovery and ransom often comes down to whether that guess was right.
8. Build a breach response plan
Decide now what the first 72 hours will look like. Know who to contact: your IT support, your malpractice insurer, and, when required, law enforcement. Know how to contain the damage by isolating affected systems and resetting credentials.
Plan for client notification, since most states have mandatory breach-notification laws. And document everything, because regulators and insurers will want a clear record of what happened and how you responded.
If that list feels like a lot to carry alone, it does not have to be. Much of this work is repeatable and delegable, and the right vetted help can run these habits day to day while you focus on practicing law.
AI Tools and Client Confidentiality, the New Frontier
Many AI tools transmit whatever you type straight to external servers. Paste a client contract into a general-purpose chatbot, and that text may be stored or used to train the model, which is a direct Rule 1.6 risk. The convenience is real, but so is the exposure.
You can use AI responsibly with a few clear rules. Read the privacy policy and terms before you commit. Choose enterprise tiers that offer data isolation and let you opt out of training. Never put client personal information into free-tier tools, and anonymize or redact whenever you can.
Document your AI use in your written policy, and favor legal-specific tools built with confidentiality in mind. In short, treat AI like any other vendor: do your due diligence, and set clear boundaries before client data is ever involved.
A Quick Word on Compliance Beyond the ABA
Your ethical duties are the floor, not the whole picture. Watch three things beyond ABA rules: your state’s data breach notification law, since most states require prompt notice to affected clients; HIPAA, if you handle protected health information in matters like personal injury or health disputes; and the CCPA, if you hold data on California residents. You do not need to master every framework. You just need to know which ones touch your practice and note them in your policy.
How Data Security Becomes a Competitive Advantage
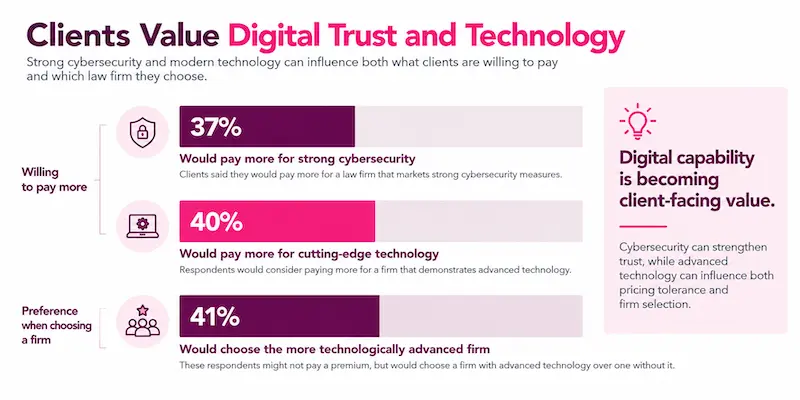
Strong security is not only a cost. It is something clients increasingly pay for. A 2025 survey of 750 United States law firm clients, commissioned by managed IT provider Integris, found that 37% would pay a premium for a firm with strong cybersecurity and 66% were hesitant to work with firms using outdated technology.
So say it out loud. Add a brief data-security statement to your engagement letters and your website, describing in plain language how you protect client information. Cautious, high-value clients notice.
There is a quieter payoff too. Solid systems and trusted help let you reclaim hours by delegating routine legal work and spend that time where it counts, with your clients.
Key Takeaways
- Start with the controls that close the biggest gaps. Put the written policy, strong authentication, encryption, and reliable backups ahead of expensive security additions.
- Control access, not just technology. Apply least privilege to software, vendors, employees, and remote support so each person or tool reaches only the data required for the job.
- Make security an ongoing operating practice. Test backups, review access, update policies, train anyone handling client files, and prepare for incidents before they happen.
- Put AI under the same governance as every other vendor. Know where client information goes, whether it can be retained or used for training, and what safeguards apply before adopting the tool.
- Make good security visible to clients. Once the controls are genuinely in place, communicate them clearly so confidentiality becomes part of the trust your firm offers.
Frequently Asked Questions
How much should a solo attorney budget for cybersecurity?
Less than you might expect. A password manager runs about USD 3 to USD 5 per month, a VPN about USD 5 to USD 10, and encrypted cloud storage roughly USD 10 to USD 15. Add cyber liability insurance at around USD 50 to USD 150 per month, and a strong baseline still lands under USD 50 per month plus your time.
Do I need cyber liability insurance as a solo attorney?
Almost certainly, yes. It typically covers breach notification costs, forensic investigation, regulatory fines, and malpractice arising from an incident, which can dwarf the premium. Expect roughly USD 50 to USD 150 per month. Before you buy, check whether your malpractice policy already includes limited cyber coverage so you do not pay twice.
Is cloud-based practice management software secure enough?
It can be, with the right vendor. Look for SOC 2 Type II certification, AES-256 encryption, role-based access controls, and a clear breach-notification policy. Reputable cloud tools often beat a local hard drive because they patch continuously and back up automatically while you focus on your cases.
How do I safely delegate client work without compromising confidentiality?
Start by defining what can be delegated: intake, scheduling, document preparation, and billing. Set data-access rules using least privilege, so each person sees only what their tasks require. Then work with vetted, trained help. A vetted Virtual Legal Assistant is screened for background, communication, and reliability, so you are not handing files to an unknown contractor.
Delegate with Confidence, Without Compromising Client Data
You became an attorney to practice law, not to run an IT department. Protecting client data does not require an enterprise budget. It requires the right habits, the right tools, and the right people, applied steadily over time.
The biggest uncontrolled variable is who touches client files. That is exactly why vetted help with least-privilege access belongs inside a secure practice, not outside it as a risk you tolerate.
At Virtual Latinos, we connect solo attorneys with pre-vetted Virtual Professionals from Latin America, the top 1% of applicants, working in U.S. time zones. You get a human-guided hiring process and a Replacement Guarantee, backed by 900+ active clients who already delegate with confidence.
Once a remote professional becomes part of your practice, protecting client data depends on how you structure their access and responsibilities. The ethical requirements for outsourcing legal work provide the foundation for setting those boundaries around confidentiality, supervision, and appropriate task assignment.
For a recurring workflow such as court-deadline and calendar management, those safeguards become concrete through controlled access, verification steps, and clear attorney oversight.